Journey A · For an SME with no IT team

Your first year of security, without an IT department.

You run the business. Security is one more thing on a list nobody has time for, and the last time something happened, a laptop went missing from a taxi. This page is the whole path: what you do in week one, what you ask somebody else to do, and what you can honestly tell a customer afterwards.

  • About 2 hours of your time across 3 weeks
  • No software installed on any staff machine
  • Works if you cannot choose a framework yet

Where you probably are today

Four starting points we hear constantly. Every one of them is a fine place to begin.

Starting point 01

“A customer asked for our security policy.”

Usually a questionnaire of 80 questions, usually from a procurement team, usually with a due date attached. You can answer the honest parts and hand off the rest — but only if someone records which is which.
Starting point 02

“Something happened and we found out late.”

A lost laptop, a staff account used from an odd location, a supplier asking for a copy of your customer list. The first useful step is usually not technical at all — it is writing down who is in charge of what.

Starting point 03

“We want the certificate our competitors have.”

Entirely reasonable. But the certificate is the last step, not the first, and chasing it first is how people end up with 200 unanswered rows and no idea what they actually hold.

Starting point 04

“Nothing has happened, so we are fine.”

The most common and the most expensive belief. Most incidents are the boring ones — a reused password, an old laptop, a departing staff member whose account stayed open.

Your first year, step by step

Six steps. The first two produce value on their own; steps three and six are where a certification becomes possible. You can stop anywhere in between.

Talk

Twenty minutes, four plain questions, no technical vocabulary.

Week 0 · 20 min

Picture

What you know, what you do not, and who owns each unknown.

Week 0 · same day

Collect

Screenshots and exports from what you already use.

Week 1 · ~1 hour

Hand off

One written request to whoever actually holds the answers.

Week 1 · 15 min

Fix

Top three actions only. Most small businesses need four changes, not forty.

Weeks 2–10

Decide

Now choose a target, with evidence in front of you instead of a brochure.

Month 3–6
  1. Answer four questions, honestly

    What does the business do and who does it serve? Roughly how many people and devices? Which system would hurt most if it stopped for a day? Who can approve security spending? “Not sure” is a complete answer and is recorded as an unknown with an owner — never as a blank.

    You do
    One call, in your own words. No system login needed.
    We do
    Turn it into scope, obligations and named owners.
    You get
    A written first picture within the hour.
  2. See the honest picture

    The dashboard opens with no framework chosen. It shows coverage by service, site and account, the highest material gaps, and a suggested set of objectives you may ignore entirely.

    You do
    Fix anything we got wrong — most answers are wrong somewhere.
    We do
    Keep known, unknown, pending and confirmed-out-of-scope apart.
    You get
    A baseline that survives your next busy month.
  3. Collect five things, not fifty

    For a business your size, the first evidence round is short: who can sign in, what is encrypted, what is backed up, what happens when someone leaves, and what you would do if something went wrong today. Each has a five-minute screen you can photograph.

    You do
    Follow the click-path table below, in order.
    We do
    Read each upload, flag secrets and stale dates, keep the source.
    You get
    Evidence with a date — which is the whole point.
  4. Hand off the rest, in writing

    Some answers genuinely belong to an IT provider, a bookkeeper or a supplier. We write the request so it cannot bounce back with a clarification: exact fields, exact scope, exact due date.

    You do
    Forward one email. You stay the point of contact, not the technician.
    We do
    Track the request, chase it, and log the answer as evidence.
    You get
    No more “waiting on IT” silence.
  5. Do the top three things only

    For most small businesses it is: turn on multi-factor authentication for the accounts that matter, get full-disk encryption on the machines that hold customer data, and turn off access for people who have left. Three changes, one weekend, a lasting difference.

    You do
    Make the change in the system you already pay for.
    We do
    Verify with a fresh read, and record who verified and when.
    You get
    A closure that a customer can read, not a promise.
  6. Now choose, if you want to

    With evidence in front of you, choosing Cyber Essentials becomes a small, calm decision instead of a gamble. You can also stay certificate-free and keep the posture picture — plenty of customers buy on that instead.

    You do
    Choose zero, one or several objectives. All are legitimate.
    We do
    Prepare the scope and evidence; the certification body does the rest.
    You get
    An answer you can put in a proposal, with its date on it.

What to collect in week one

Six items, each with the exact place to look. None of them needs an administrator, a licence or a new account.

Week-one collection list · every item is one dated screen or one exported file
Item Where it is Who does it What it proves What it does not prove
Sign-in protection Google Admin → Security → 2SV; Microsoft 365 admin → Security settings You, with the account you already log in with What protection is configured for your accounts That every person actually completes it
One laptop's protection status Windows Security → Virus & threat protection → Protection history Whoever sits at that machine The state of that one device on that one day The state of the other laptops you have not looked at
Disk encryption macOS: System Settings → Privacy & Security → FileVault · Windows: Settings → Privacy → Device encryption The person at the machine Whether encryption is switched on for that device That the recovery key is stored somewhere safe
Who can get in Your Google/Microsoft admin roster; your payment and storefront accounts You Which accounts exist and who holds them Whether each holder is the right holder
Your backup Your backup provider's last successful run, plus the date of your last restore test You or your bookkeeper That a backup job ran That your data can actually be restored
Who is accountable A one-page note: names, roles, contact numbers, escalation order You That a decision has an owner That the plan has been rehearsed
Photograph or screenshot, do not export. A dated screen showing a setting is a legitimate first artefact for a business your size. Export everything when someone technical is available — but do not let the absence of an export stall the whole exercise.

The request to send your IT provider

This is the artefact people tell us they did not know existed. Copy it, fill the four blanks and send it. It removes the round trip where the provider asks what you actually need.

Hand-off request · template

Request for security evidence

Copy this into an email or a ticket. Everything we need is in the table.

# What we need Format Scope Due
1 List of devices you look after for us CSV or a dated export All devices with company data [date]
2 Whether full-disk encryption is on, per device Yes / No / Unknown, per device Same list [date]
3 Antivirus or protection status and last update date Export or screenshot Same list [date]
4 Who holds administrator rights on our accounts Names and roles Our accounts only [date]
5 Date of the last backup restore test One line + the record it refers to Our data [date]

Please do not include passwords, private or recovery keys, tokens, connection strings, Wi-Fi passphrases, session cookies, mailbox contents or full device configurations. If any of these appear in an export, delete them from the file and re-export.

If the answer is “we do not know”. That is a usable answer. It becomes an unknown with an owner and a date, and it stops being a silent gap. If the ideal export does not exist, the fallback ladder is: the system's own export → a dated screenshot → a written statement from the accountable role → a dated attestation from the supplier → record it as unknown.

A worked example: Selegie Roastworks

Composite example · not a real customer

Eleven staff, a shared warehouse, a roastery, one storefront system and no IT department. Here is what the first twelve weeks actually looked like.

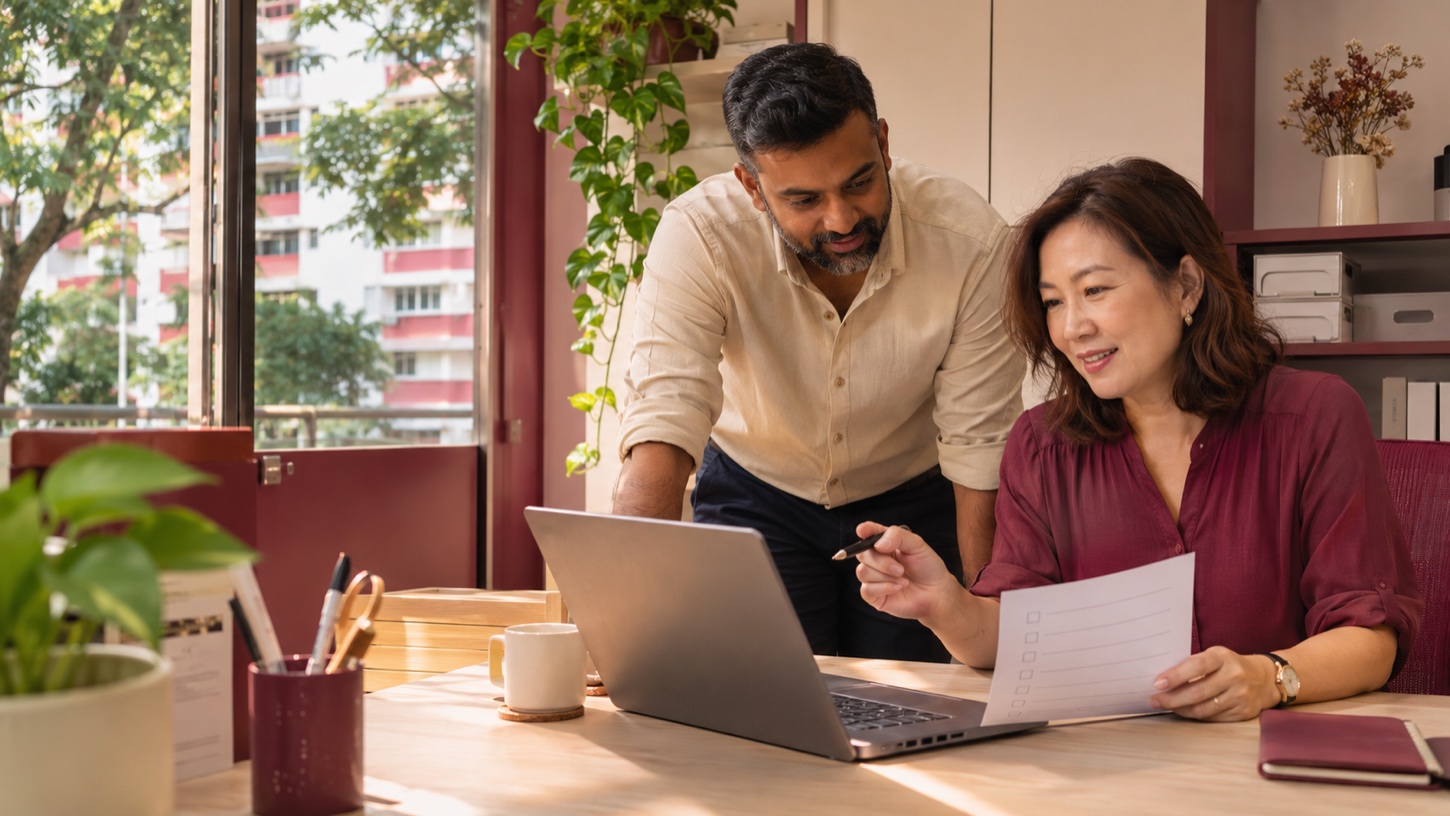
Two colleagues working together over a printed document at a desk
The whole first round of evidence for a business this size was collected by two people, in person, over three weeks.
  • Week 0 · Tuesday, 09:40

    The call

    The founder answered the four questions in nineteen minutes. Nobody logged into anything. The only decision made on the call was who would be asked about the two laptops that had “disappeared” since March.

  • Week 0 · same day, 11:15

    The first picture

    Six known facts, eleven unknowns, one owner per unknown. The suggested objective was Cyber Essentials — and it stayed a suggestion for a month, because the founder wanted to see what was actually missing first.

  • Week 1

    Two screenshots

    The Google Workspace security page and the Protection-history screen on the office laptop. One of the two laptops had protection switched off since January. Nobody had known.

  • Week 1

    One hand-off request

    Five rows sent to their IT provider: device list, encryption status, protection status, administrator list, last restore test. Three came back within four days. The restore test had never been done — so that row became an unknown with a due date, not a failure.

  • Weeks 2–6

    Three changes

    Passkeys for the Shopify and Google admin accounts. Two staff laptops replaced with managed machines with encryption on. Access removed for a former part-time roaster, which nobody had done in nine months.

  • Week 12

    The picture again

    Two unknowns left: the shop-floor tablet and the customer-data backup restore test. Both had an owner and a date. The founder’s words in the review meeting: “I now know what I don't know, which is more than I did in March.”

What Cyber Essentials asks — and what it does not

Plainly, so that nothing surprises you later. This is the scheme’s own shape, not our opinion of it.

What the scheme covers

  • A defined set of baseline controls for the organisation and its systems in scope.
  • A self-assessment you complete, then prepare for independent desktop verification.
  • Two-year validity for the mark, once it is issued.
  • Requirements and recommendations tracked separately — the recommendations are advisory.

What it does not do

  • It does not verify that every recommendation has been implemented.
  • It does not certify a single device — it certifies a scoped organisation and its controls.
  • It does not replace sector rules, contracts or your own customer obligations.
  • It does not tell you which of your systems actually matter most to your business.
The honest bit. Security Passport helps you gather and organise the evidence. It cannot grant the mark, cannot decide your scope for you and cannot convert “not sure” into a pass. The certification body is the only party that can issue one.

What this does not do

Install anything

No endpoint agent, no extra security licence, no new software on a staff machine.

Touch your money

No purchase, no renewal, no change to a service you already pay for.

Read anything first

No account is connected until you have seen an itemised list of what would be read.

Ask for your passwords

Not for your Google, Microsoft, bank, payroll or supplier accounts. Ever.

Fill in what you do not know

Unknown is recorded as unknown, with an owner and a request date.

Promise a certificate

We prepare evidence and scope. The certification body decides and issues.

Start where Selegie started.

Twenty minutes, four questions, and a written picture of where you stand — with every unknown carrying an owner and a date.